DoD 8140 Certification List and Chart: 56 Certs by Work Role
By The Defense Compliance Report Editorial Team · Updated September 2026
The DoD 8140 certification list in Matrix V2.1 (effective Sept. 19, 2025) names 56 commercial certifications. GSEC counts in 22 of its 37 in-scope work roles, more than any other certification; Security+ counts in 19, none at Advanced, according to The Defense Compliance Report's September 2026 analysis. Below: every cert by role, plus a lookup. Source and data.
Scope: The 37 roles are in V2.1's published DoD CIO qualification scope. Of the 56 commercial certs in the workbook, 55 appear there; GCTI appears only in pending-validation roles. This is a certification reference, not a ruling that a person is fully qualified. Scope and method.
Browse the full list · Find a work role · Check your certs · Download the CSV
Key DoD 8140 certification statistics
- 22 of 37 work roles: GSEC is listed in 22 of the 37 work roles in DoD CIO-approved workforce elements, more than any other certification (The Defense Compliance Report analysis of DoD 8140 Matrix V2.1, September 2026). Source.
- 19 roles, none at Advanced in V2.1: Security+ is listed in 19 of those 37 work roles, every time at the Intermediate level. It has no Advanced listing in V2.1 (The Defense Compliance Report analysis of Matrix V2.1, September 2026). Source.
- 56 certifications: The DoD 8140 Foundational Qualification Matrix Version 2.1, effective Sept. 19, 2025, lists 56 commercial certifications from 10 vendors, plus 4 Defense Acquisition Workforce Improvement Act (DAWIA) credential labels from Defense Acquisition University (DoD CIO, Matrix V2.1). Source.
- 17 certs for CMMC assessors: 17 certifications meet the Work Role 612 bar that 32 CFR 170.11 sets for CMMC Certified Assessors (Intermediate or higher): 9 listed at Intermediate and 8 at Advanced (The Defense Compliance Report analysis of Matrix V2.1, September 2026). Source.
- 12 down to 8 for Lead CCAs: V2.1 cut the list of Work Role 612 certs at the Advanced level, the level a Lead CCA needs, from 12 to 8 (DoD's V2.1 change log, counted by The Defense Compliance Report). Source.
- 3 listed, 13 count: For System Administrator (451), the matrix lists 3 certifications at Basic, but 13 count at Basic once higher-level listings are included under DoD's same-role rule (The Defense Compliance Report analysis of Matrix V2.1 and DoDM 8140.03). Source.
- 13 roles at Advanced: GSLC is listed at the Advanced level in 13 approved work roles, more than any other certification. CISSP is listed in 10, all at Advanced (The Defense Compliance Report analysis of Matrix V2.1). Source.
- 32 of 35 old certs: 32 of the 35 certifications on the January 30, 2024 archived DoD 8570 baseline chart also appear in the September 19, 2025 V2.1 workbook. HCISPP, SCYBER, and CCNA-Security are not (The Defense Compliance Report comparison, September 2026). Source.
- 24 absent from the 2024 chart: 24 of the 56 commercial certs in the September 19, 2025 V2.1 workbook do not appear in the January 30, 2024 archived 8570 chart (The Defense Compliance Report comparison, September 2026). This is not a count of certs never approved under 8570. Source.
- 25 lowered, 0 raised: V2.1's certification change log shows 21 listings added, 25 moved to a lower level, and 2 removed. None moved up (DoD Matrix V2.1 change log, counted by The Defense Compliance Report). Source.
- 19 of 56 from GIAC: GIAC has more certifications on the V2.1 list than any other vendor (The Defense Compliance Report count of the V2.1 Certification Index). Source.
- 3 roles with no cert: 3 of the 37 approved work roles list no certification at all: 462, 731, and 901 (DoD Matrix V2.1). Source.
- Feb. 15, 2023: DoD Manual 8140.03 took effect and canceled the DoD 8570.01-M manual (DoDM 8140.03). Source.
- 9 and 12 months: The September 1, 2026 supplemental guidance starts the military/civilian foundational and resident qualification periods at issuance of the DoD 8140 Letter of Designation. Letter issuance is at component discretion; the 2023 manual states assignment as the start. Confirm the recorded start with the component (DoD 8140 Supplemental Guidance V1.1, pp. 4–5). Source.
- May 27, 2026 contractor update: DoD's contractor memo directs components to ensure contract support meets the assigned DCWF work-role qualifications and to update contracts. It says deviation text removing the old 8570 references and DFARS 252.239-7001 took effect February 1, 2026. The still-visible old clause is not the whole current rule. Source.
On this page: The full list · Check your certs · Chart by work role · Higher levels count lower · Most-accepted certs · Security+ · CMMC assessors (612) · ISSM (722) · 8570 and IAT II · V2.1 changes · How it works · Contractors · Method · Cite · Download · FAQ · Sources
What certifications are on the DoD 8140 list?
The latest matrix listed in the official library on September 29, 2026, Version 2.1 (effective Sept. 19, 2025), lists 56 commercial certifications from 10 vendors, plus 4 Defense Acquisition University credentials. A certification counts only for the work roles and levels DoD lists it for. 55 of the 56 appear in at least one of the 37 work roles in V2.1's published CIO scope; GCTI appears only in roles still pending validation.
Here's how to read the table. "Approved work roles" means the 37 roles in V2.1's published CIO scope throughout this page. The count shows how many list the cert at any level. "Highest level listed" is the top level it reaches in any of them. A cert at the bottom of this table isn't worse. It's narrower.
| Rank | Cert | Name (shortened where shown) | Vendor | Approved work roles (of 37) | Roles where listed at Advanced | Highest level listed | Pending-validation roles | On Jan. 30, 2024 8570 chart? |
|---|---|---|---|---|---|---|---|---|
| 1 | GSEC | GIAC Security Essentials Certification | GIAC | 22 | 0 | Intermediate | 3 | Yes |
| 2 | Security+ | CompTIA Security+ | CompTIA | 19 | 0 | Intermediate | 1 | Yes |
| 3 | SecurityX / CASP+ | CompTIA SecurityX (formerly CASP+) | CompTIA | 17 | 9 | Advanced | 0 | Yes |
| 4 | GCSA | GIAC Cloud Security Automation | GIAC | 14 | 8 | Advanced | 1 | No |
| 4 | CCSP | Certified Cloud Security Professional | ISC2 | 14 | 7 | Advanced | 1 | Yes |
| 4 | Cloud+ | CompTIA Cloud+ | CompTIA | 14 | 0 | Intermediate | 1 | Yes |
| 7 | GSLC | GIAC Security Leadership Certification | GIAC | 13 | 13 | Advanced | 1 | Yes |
| 8 | CISM | Certified Information Security Manager | ISACA | 12 | 12 | Advanced | 1 | Yes |
| 8 | SSCP | Systems Security Certified Practitioner | ISC2 | 12 | 2 | Advanced | 2 | Yes |
| 10 | GICSP | Global Industrial Cyber Security Professional | GIAC | 11 | 8 | Advanced | 1 | Yes |
| 11 | CISSP | Certified Information Systems Security Professional | ISC2 | 10 | 10 | Advanced | 1 | Yes |
| 11 | CCISO | Certified Chief Information Security Officer | EC-Council | 10 | 9 | Advanced | 1 | Yes |
| 11 | CISSO | Certified Information Systems Security Officer | Mile2 | 10 | 7 | Advanced | 1 | No |
| 14 | CISSP-ISSEP | CISSP – Engineering Professional | ISC2 | 9 | 9 | Advanced | 1 | Yes |
| 14 | CFR | CyberSec First Responder | CertNexus | 9 | 7 | Advanced | 0 | Yes |
| 14 | GFACT | GIAC Foundational Cybersecurity Technologies | GIAC | 9 | 6 | Advanced | 0 | No |
| 14 | RCCE Level 1 | Rocheston Certified Cybersecurity Engineer Level 1 | Rocheston | 9 | 6 | Advanced | 3 | No |
| 14 | PenTest+ | CompTIA PenTest+ | CompTIA | 9 | 1 | Advanced | 1 | Yes |
| 14 | CND | Certified Network Defender | EC-Council | 9 | 0 | Intermediate | 1 | Yes |
| 20 | CySA+ | CompTIA CySA+ | CompTIA | 8 | 7 | Advanced | 2 | Yes |
| 20 | GCLD | GIAC Cloud Security Essentials | GIAC | 8 | 3 | Advanced | 1 | No |
| 22 | GCIA | GIAC Certified Intrusion Analyst | GIAC | 7 | 7 | Advanced | 0 | Yes |
| 22 | FITSP-M | Federal IT Security Professional-Manager-NG | FITSI | 7 | 6 | Advanced | 0 | No |
| 22 | GISF | GIAC Information Security Fundamentals | GIAC | 7 | 3 | Advanced | 1 | No |
| 22 | CEH | Certified Ethical Hacker | EC-Council | 7 | 1 | Advanced | 0 | Yes |
| 26 | CISA | Certified Information Systems Auditor | ISACA | 6 | 6 | Advanced | 0 | Yes |
| 26 | GCIH | GIAC Certified Incident Handler | GIAC | 6 | 2 | Advanced | 3 | Yes |
| 26 | GDSA | GIAC Defensible Security Architect | GIAC | 6 | 2 | Advanced | 0 | No |
| 29 | GCFA | GIAC Certified Forensic Analyst | GIAC | 5 | 5 | Advanced | 2 | Yes |
| 29 | FITSP-A | Federal IT Security Professional-Auditor-NG | FITSI | 5 | 3 | Advanced | 0 | No |
| 29 | CC | Certified in Cybersecurity | ISC2 | 5 | 0 | Basic | 0 | No |
| 29 | CGRC/CAP | Certified in Governance, Risk and Compliance (formerly CAP) | ISC2 | 5 | 0 | Intermediate | 0 | Yes |
| 29 | Network+ | CompTIA Network+ | CompTIA | 5 | 0 | Basic | 0 | Yes |
| 34 | CCNP Security | Cisco CCNP Security | Cisco | 4 | 4 | Advanced | 0 | Yes |
| 34 | CISSP-ISSAP | CISSP – Architecture Professional | ISC2 | 4 | 4 | Advanced | 1 | Yes |
| 34 | FITSP-D | Federal IT Security Professional-Designer-NG | FITSI | 4 | 2 | Advanced | 0 | No |
| 34 | FITSP-O | Federal IT Security Professional-Operator-NG | FITSI | 4 | 2 | Advanced | 1 | No |
| 34 | GCED | GIAC Certified Enterprise Defender | GIAC | 4 | 1 | Advanced | 0 | Yes |
| 34 | CSSLP | Certified Secure Software Lifecycle Professional | ISC2 | 4 | 0 | Intermediate | 1 | Yes |
| 34 | GMON | GIAC Continuous Monitoring | GIAC | 4 | 0 | Intermediate | 0 | No |
| 41 | CISSP-ISSMP | CISSP – Management Professional | ISC2 | 3 | 3 | Advanced | 0 | Yes |
| 41 | GCFE | GIAC Certified Forensic Examiner | GIAC | 3 | 3 | Advanced | 0 | No |
| 41 | GSNA | GIAC Systems and Network Auditor | GIAC | 3 | 2 | Advanced | 1 | Yes |
| 41 | A+ | CompTIA A+ | CompTIA | 3 | 0 | Basic | 0 | Yes |
| 41 | CEH(P) | Certified Ethical Hacker (Practical) | EC-Council | 3 | 0 | Intermediate | 0 | No |
| 41 | CHFI | Computer Hacking Forensics Investigator | EC-Council | 3 | 0 | Intermediate | 0 | Yes |
| 41 | GRID | GIAC Response and Industrial Defense | GIAC | 3 | 0 | Intermediate | 0 | No |
| 48 | CBROPS | Cisco CyberOps Associate | Cisco | 2 | 1 | Advanced | 0 | Yes |
| 48 | CSC | Cyber Secure Coder | CertNexus | 2 | 0 | Intermediate | 0 | No |
| 50 | CCNA | Cisco Certified Network Associate | Cisco | 1 | 1 | Advanced | 0 | No |
| 50 | CCNP Enterprise | Cisco CCNP Enterprise | Cisco | 1 | 1 | Advanced | 0 | No |
| 50 | GPEN | GIAC Penetration Tester | GIAC | 1 | 1 | Advanced | 4 | No |
| 50 | GREM | GIAC Reverse Engineering Malware | GIAC | 1 | 1 | Advanced | 0 | No |
| 50 | CPTE | Certified Penetration Testing Engineer | Mile2 | 1 | 0 | Intermediate | 0 | No |
| 50 | ECIH | Certified Incident Handler | EC-Council | 1 | 0 | Intermediate | 0 | No |
| 56 | GCTI | GIAC Cyber Threat Intelligence | GIAC | 0 | 0 | — | 4 | No |
Source: DoD 8140 Foundational Qualification Matrix V2.1, effective Sept. 19, 2025, Certification Repository and Certification Index sheets; counts by The Defense Compliance Report, checked Sept. 29, 2026. "Pending-validation roles" are roles in elements the workbook marks Tentative. 8570 comparison: DoD Approved 8570 Baseline Certifications (archived).
The matrix also lists four DAWIA credentials. They come from the Defense Acquisition Workforce program, not a commercial exam, so we keep them out of the 56.
| DAWIA credential (Defense Acquisition University) | Approved work roles | Level listed |
|---|---|---|
| DAWIA PM Advanced | 801 Program Manager, 802 IT Project Manager | Advanced |
| DAWIA PM Practitioner | 801 Program Manager, 802 IT Project Manager | Intermediate |
| DAWIA LCL Advanced | 803 Product Support Manager | Advanced |
| DAWIA LCL Foundational | 803 Product Support Manager | Intermediate |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository sheet; checked Sept. 29, 2026.
Which DoD 8140 work roles does my certification cover?
Pick the certifications you hold, and the lookup shows every approved work role they count for and the highest level they reach. Security+ alone counts in 19 roles, up to Intermediate. Add CySA+ and you reach 22 roles, 7 of them at Advanced.
You can also flip it. Pick a work role and a level, and you get every certification that counts there. Results say whether a cert is listed at that exact level or counts because it's listed higher in the same role.
One warning before you use it. "No match here" means this V2.1 extract has no match for that cert, role, and level. It doesn't mean you're disqualified. Degrees and training can also qualify you, and your cyber workforce manager makes the final call.
Explore certification listings by credential or work role
Compare the dated Matrix V2.1 certification path in this browser using public static CSVs. No account, form, or email is requested. Search terms and selections stay in this browser; they are not saved or sent, and no personal data is collected. A listing is only one foundational qualification option; it does not establish full qualification.
DoD 8140 chart: which certifications count for each work role?
Each of the 37 approved work roles has its own list at Basic, Intermediate, and Advanced. 34 roles list at least one certification; 462 Control Systems Security Specialist, 731 Cyber Legal Advisor, and 901 Executive Cyber Leader list none. A certification listed at a higher level also counts at the lower levels of the same role.
To use the chart, find your role code and read across. The first three list columns show what DoD printed at each level. The last column counts the listed credentials, including DAWIA labels where shown, once higher listings roll down. It covers only the foundational certification option, not full qualification.
Cybersecurity work roles (13)
| Code | Work role | Listed at Basic | Listed at Intermediate | Listed at Advanced | Credentials that count at Basic / Int. / Adv. |
|---|---|---|---|---|---|
| 212 | Cyber Defense Forensics Analyst | — | CHFI, RCCE Level 1 | CFR, CySA+, GCFA, GCFE, GREM, PenTest+ | 8 / 8 / 6 |
| 462 | Control Systems Security Specialist | — | — | — | 0 / 0 / 0 |
| 511 | Cyber Defense Analyst | CC, CEH, GFACT, GISF | CEH(P), Cloud+, FITSP-O, GCED, GDSA, GMON, GRID, GSEC, PenTest+, Security+ | CBROPS, CFR, CySA+, GCFA, GCIA, GICSP | 20 / 16 / 6 |
| 521 | Cyber Defense Infrastructure Support Specialist | A+, CC, CND, GCLD, GDSA, GFACT, Network+ | CEH, Cloud+, CySA+, GMON, GRID, GSEC, PenTest+, Security+, SSCP | CISSP-ISSAP, CISSP-ISSEP, GCIA, GICSP | 20 / 13 / 4 |
| 531 | Cyber Defense Incident Responder | CC, GDSA, GISF | CBROPS, CCSP, CEH, CEH(P), Cloud+, ECIH, FITSP-O, GCED, GCIH, GRID, GSEC, PenTest+, RCCE Level 1, Security+ | CFR, CySA+, GCFA, GCIA, GICSP | 22 / 19 / 5 |
| 541 | Vulnerability Assessment Analyst | CEH | CEH(P), Cloud+, CPTE, FITSP-A, GCED, GCIH, GCSA, GICSP, GSEC, PenTest+, RCCE Level 1, Security+ | CFR, CISA, CISM, CySA+, GPEN, GSNA | 19 / 18 / 6 |
| 611 | Authorizing Official/Designated Representative | — | CCSP, CGRC/CAP, Cloud+, GSEC | CCISO, CISM, CISSP, CISSP-ISSEP, CISSP-ISSMP, FITSP-M, GCSA, GSLC | 12 / 12 / 8 |
| 612 | Security Control Assessor | — | CGRC/CAP, CISSO, Cloud+, FITSP-A, GCSA, GSEC, PenTest+, Security+, SecurityX / CASP+ | CCISO, CISA, CISM, CISSP, CISSP-ISSEP, CySA+, GSLC, GSNA | 17 / 17 / 8 |
| 622 | Secure Software Assessor | GCLD | CSC, CSSLP, GCSA, GSEC, Security+ | CISSP-ISSEP | 7 / 6 / 1 |
| 631 | Information Systems Security Developer | CC, CND, GISF, SSCP | CCSP, Cloud+, CSC, GCLD, GCSA, GSEC, SecurityX / CASP+ | CISSP-ISSEP, FITSP-D | 13 / 9 / 2 |
| 652 | Security Architect | GCLD, GISF | CCSP, CISSO, Cloud+, CSSLP, FITSP-D, GCSA, GMON, GSEC, SecurityX / CASP+ | CCNP Enterprise, CISM, CISSP-ISSAP, CISSP-ISSEP, GCIA, GDSA, GICSP | 18 / 16 / 7 |
| 722 | Information Systems Security Manager | CC | CCISO, CCSP, CGRC/CAP, CISSO, Cloud+, GCSA, GMON, GSEC, Security+, SecurityX / CASP+, SSCP | CISM, CISSP, CISSP-ISSMP, FITSP-M, GCIA, GCIH, GICSP, GSLC | 20 / 19 / 8 |
| 723 | COMSEC Manager | — | GSEC | CISM, CISSO, FITSP-M, GCIH, GCSA, GICSP, GSLC | 8 / 8 / 7 |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository and Matrix Outline & Notes sheets; last column calculated by The Defense Compliance Report under DoDM 8140.03 section 3.2.b(1)(c)5.a; checked Sept. 29, 2026.
Cyber IT work roles (10)
| Code | Work role | Listed at Basic | Listed at Intermediate | Listed at Advanced | Credentials that count at Basic / Int. / Adv. |
|---|---|---|---|---|---|
| 411 | Technical Support Specialist | A+, Network+ | CND, GFACT, GSEC, Security+ | CCNP Security, CISA, FITSP-O, GICSP, SecurityX / CASP+, SSCP | 12 / 10 / 6 |
| 421 | Database Administrator | — | Cloud+, GSEC, Security+, SSCP | CCNP Security, CISA, CISSP, CISSP-ISSAP, CISSP-ISSEP, SecurityX / CASP+ | 10 / 10 / 6 |
| 431 | Knowledge Manager | — | Security+, SSCP | — | 2 / 2 / 0 |
| 441 | Network Operations Specialist | CND, Network+ | CEH, Cloud+, GCIH, GICSP, GSEC, Security+, SSCP | CCNA, CCNP Security, CCSP, GCED, GCIA, GCLD, GDSA, GFACT, SecurityX / CASP+ | 18 / 16 / 9 |
| 451 | System Administrator | A+, CND, Network+ | Cloud+, GICSP, GSEC, Security+, SSCP | CCNP Security, CCSP, FITSP-O, GFACT, SecurityX / CASP+ | 13 / 10 / 5 |
| 632 | Systems Developer | CND | CSSLP, GCLD, GSEC | FITSP-D, GCSA, GISF, SSCP | 8 / 7 / 4 |
| 641 | Systems Requirements Planner | CND | CCSP, CFR, FITSP-M, GSEC, Security+, SSCP | GCSA, GSLC, SecurityX / CASP+ | 10 / 9 / 3 |
| 651 | Enterprise Architect | CND | CCSP, Cloud+, CSSLP, FITSP-D, GDSA, GSEC, SecurityX / CASP+ | CISSO, CISSP-ISSAP, CISSP-ISSEP, GCIA, GCLD, GCSA, GICSP | 15 / 14 / 7 |
| 661 | Research & Development Specialist | — | Security+ | CEH, GCLD, RCCE Level 1, SecurityX / CASP+ | 5 / 5 / 4 |
| 671 | System Testing and Evaluation Specialist | CND, Network+ | CEH, CFR, Cloud+, GSEC, PenTest+, Security+, SSCP | CCSP | 10 / 8 / 1 |
Source: official V2.1 workbook, Certification Repository and Matrix Outline & Notes; same-role rule in DoDM 8140.03. Checked Sept. 29, 2026.
Cyber enabler work roles (14)
| Code | Work role | Listed at Basic | Listed at Intermediate | Listed at Advanced | Credentials that count at Basic / Int. / Adv. |
|---|---|---|---|---|---|
| 211 | Forensics Analyst | — | CHFI, PenTest+ | CFR, CySA+, GCFA, GCFE, RCCE Level 1 | 7 / 7 / 5 |
| 221 | Cyber Crime Investigator | GCIH | CHFI, PenTest+ | CFR, CySA+, GCFA, GCFE, SecurityX / CASP+ | 8 / 7 / 5 |
| 711 | Cyber Instructional Curriculum Developer | — | GSEC | — | 1 / 1 / 0 |
| 712 | Cyber Instructor | — | — | CISSO | 1 / 1 / 1 |
| 731 | Cyber Legal Advisor | — | — | — | 0 / 0 / 0 |
| 732 | Privacy Compliance Manager | — | — | CISSO, GSLC | 2 / 2 / 2 |
| 751 | Cyber Workforce Developer and Manager | — | Security+ | CCISO, CCSP, CFR, CISM, CISSP, GSLC, SecurityX / CASP+ | 8 / 8 / 7 |
| 752 | Cyber Policy and Strategy Planner | — | Security+ | CCISO, CCSP, CISM, CISSO, CISSP, GSLC, SecurityX / CASP+ | 8 / 8 / 7 |
| 801 | Program Manager | — | CGRC/CAP, DAWIA PM Practioner, SecurityX / CASP+ | CCISO, CISM, CISSO, CISSP, DAWIA PM Advanced, GFACT, GSLC, RCCE Level 1 | 11 / 11 / 8 |
| 802 | IT Project Manager | — | DAWIA PM Practioner, GSEC, Security+, SecurityX / CASP+ | CCISO, CCSP, CISA, CISM, CISSP, CISSP-ISSEP, CISSP-ISSMP, DAWIA PM Advanced, FITSP-A, FITSP-M, GFACT, GSLC, RCCE Level 1 | 17 / 17 / 13 |
| 803 | Product Support Manager | — | DAWIA LCL Foundational | CCISO, DAWIA LCL Advanced, GCSA, GFACT, GISF, GSLC, RCCE Level 1 | 8 / 8 / 7 |
| 804 | IT Investment/Portfolio Manager | — | — | CCISO, CISM, CISSO, CISSP, FITSP-A, FITSP-M, GCSA, GFACT, GSLC | 9 / 9 / 9 |
| 805 | IT Program Auditor | — | CGRC/CAP, GSEC, GSNA, Security+, SecurityX / CASP+, SSCP | CCISO, CCSP, CISA, CISM, CISSP, FITSP-A, FITSP-M, GCSA, GISF, GSLC, RCCE Level 1 | 17 / 17 / 11 |
| 901 | Executive Cyber Leader | — | — | — | 0 / 0 / 0 |
Source: official V2.1 workbook, Certification Repository and Matrix Outline & Notes; same-role rule in DoDM 8140.03. Checked Sept. 29, 2026.
Enabler roles have an extra door. DoD's 40-hour Cyber 101 course satisfies foundational qualification for cyber enabler work roles at all three levels, according to the V2.1 matrix notes. That's why 731 and 901 can have no certification listed and still have a path.
Work roles still pending DoD validation
The workbook lists 74 work roles in all. The other 37 sit in four elements the workbook marks "Tentative": cyber effects, intelligence (cyber), data/AI, and software engineering. Other offices own those elements. Eleven of those roles have certification rows outside this release's published CIO scope. They are pending-validation records in this workbook, not qualification rules for those elements. Use the responsible office's current guidance for those roles.
| Code | Work role | Element | Owner | Certs listed (pending validation) |
|---|---|---|---|---|
| 111 | All-Source Analyst | Intel (Cyber) | OUSD(I&S) | Advanced: CySA+, GCTI, RCCE Level 1 |
| 121 | Exploitation Analyst | Cyber Effects | PCA/USCYBERCOM | Advanced: GCIH, GPEN, PenTest+ |
| 131 | Joint Targeting Analyst | Cyber Effects | PCA/USCYBERCOM | Advanced: GPEN |
| 132 | Target Digital Network Analyst | Cyber Effects | PCA/USCYBERCOM | Advanced: GCIH, GPEN |
| 311 | All-Source Collection Manager | Intel (Cyber) | OUSD(I&S) | Advanced: GCFA, GCTI |
| 312 | All-Source Collection Requirements Manager | Intel (Cyber) | OUSD(I&S) | Advanced: GCFA, GCTI |
| 331 | Cyber Intelligence Planner | Intel (Cyber) | OUSD(I&S) | Advanced: GCTI |
| 332 | Cyber Operations Planner | Cyber Effects | PCA/USCYBERCOM | Advanced: GCIH, GPEN, RCCE Level 1 |
| 422 | Data Analyst | Data/AI | CDAO | Intermediate: GSEC, SSCP; Advanced: CCISO, CISM, CISSP, GSLC |
| 461 | Systems Security Analyst | Software Engineering | OUSD(R&E) | Basic: CND, SSCP; Intermediate: CCSP, Cloud+, GICSP, GISF, GSEC, Security+; Advanced: CISSO, CISSP-ISSEP, CySA+, FITSP-O, GCLD, GCSA, GSNA, RCCE Level 1 |
| 621 | Software Developer | Software Engineering | OUSD(R&E) | Intermediate: CSSLP, GSEC; Advanced: CISSP-ISSAP |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository and the V2.1 scope statement (records outside the published CIO scope); checked Sept. 29, 2026.
Does a higher-level certification count at Basic or Intermediate?
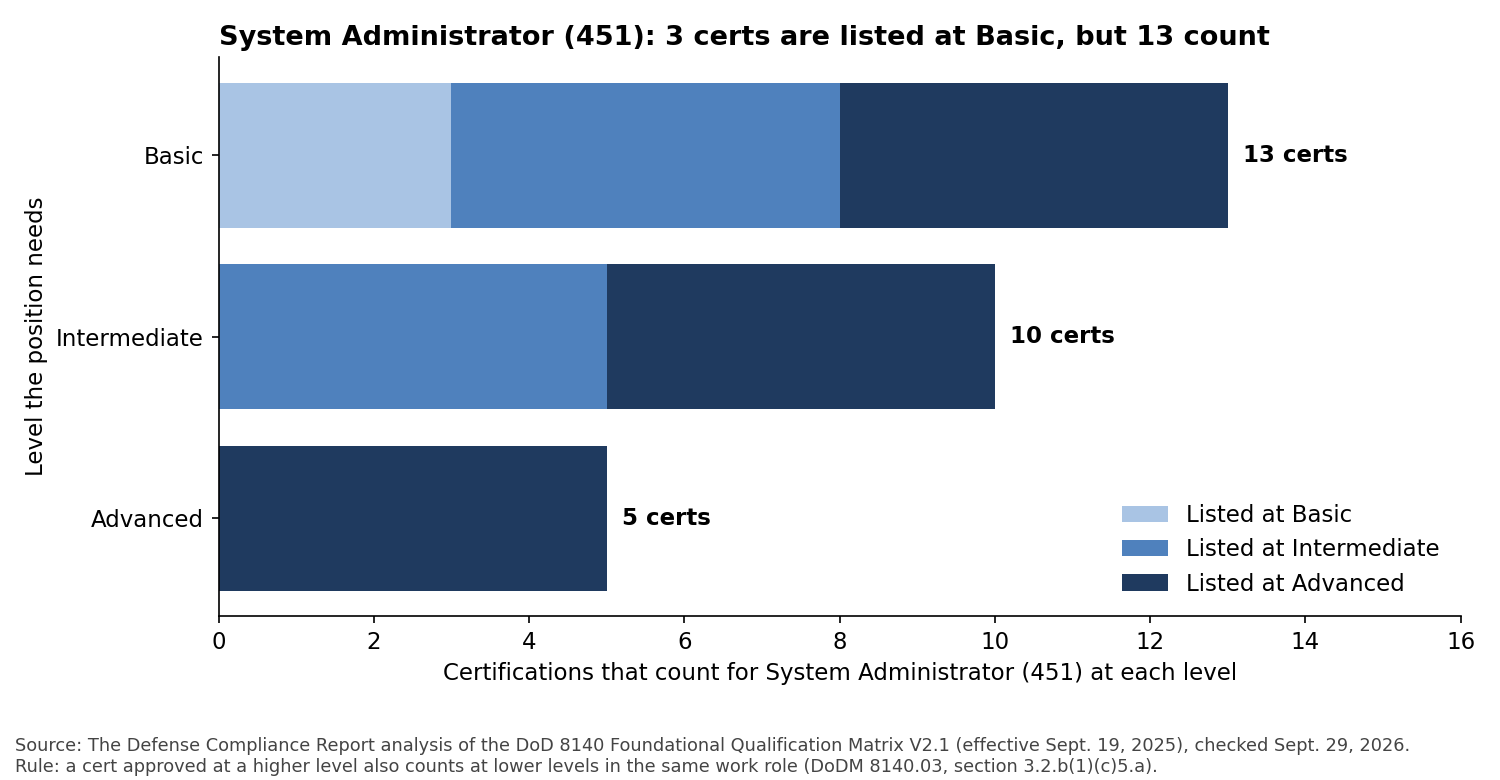
Yes, inside the same work role. DoD Manual 8140.03 says certifications approved at a higher level also apply to lower levels within the work role. So for System Administrator (451), the matrix lists 3 certifications at Basic, but 13 count at Basic.
Reading only the Basic box misses the higher-level options. You see three names, but that is not the whole Basic list. But every cert in the Intermediate and Advanced boxes counts at Basic too.
Here's the math for 451. Basic: 3 listed at Basic + 5 at Intermediate + 5 at Advanced = 13. Intermediate: 5 + 5 = 10. Advanced: 5.
| Level the position needs | Listed at Basic | Listed at Intermediate | Listed at Advanced | Certs that count |
|---|---|---|---|---|
| Basic | 3 | 5 | 5 | 13 |
| Intermediate | 0 | 5 | 5 | 10 |
| Advanced | 0 | 0 | 5 | 5 |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository sheet; rule from DoDM 8140.03, section 3.2.b(1)(c)5.a; calculated by The Defense Compliance Report, checked Sept. 29, 2026.
Say your position is coded 451 at Basic and you hold CCSP. DoD lists CCSP at Advanced for 451, so it counts for your Basic position.
The rule never jumps roles, though. A cert listed for 451 says nothing about 511 or any other role. Across all 37 approved roles, the 384 listings DoD printed become 920 level matches once they roll down. The extra 536 aren't new approvals. They're the same approvals, read the way the manual says to read them.
Which certification counts in the most DoD 8140 work roles?
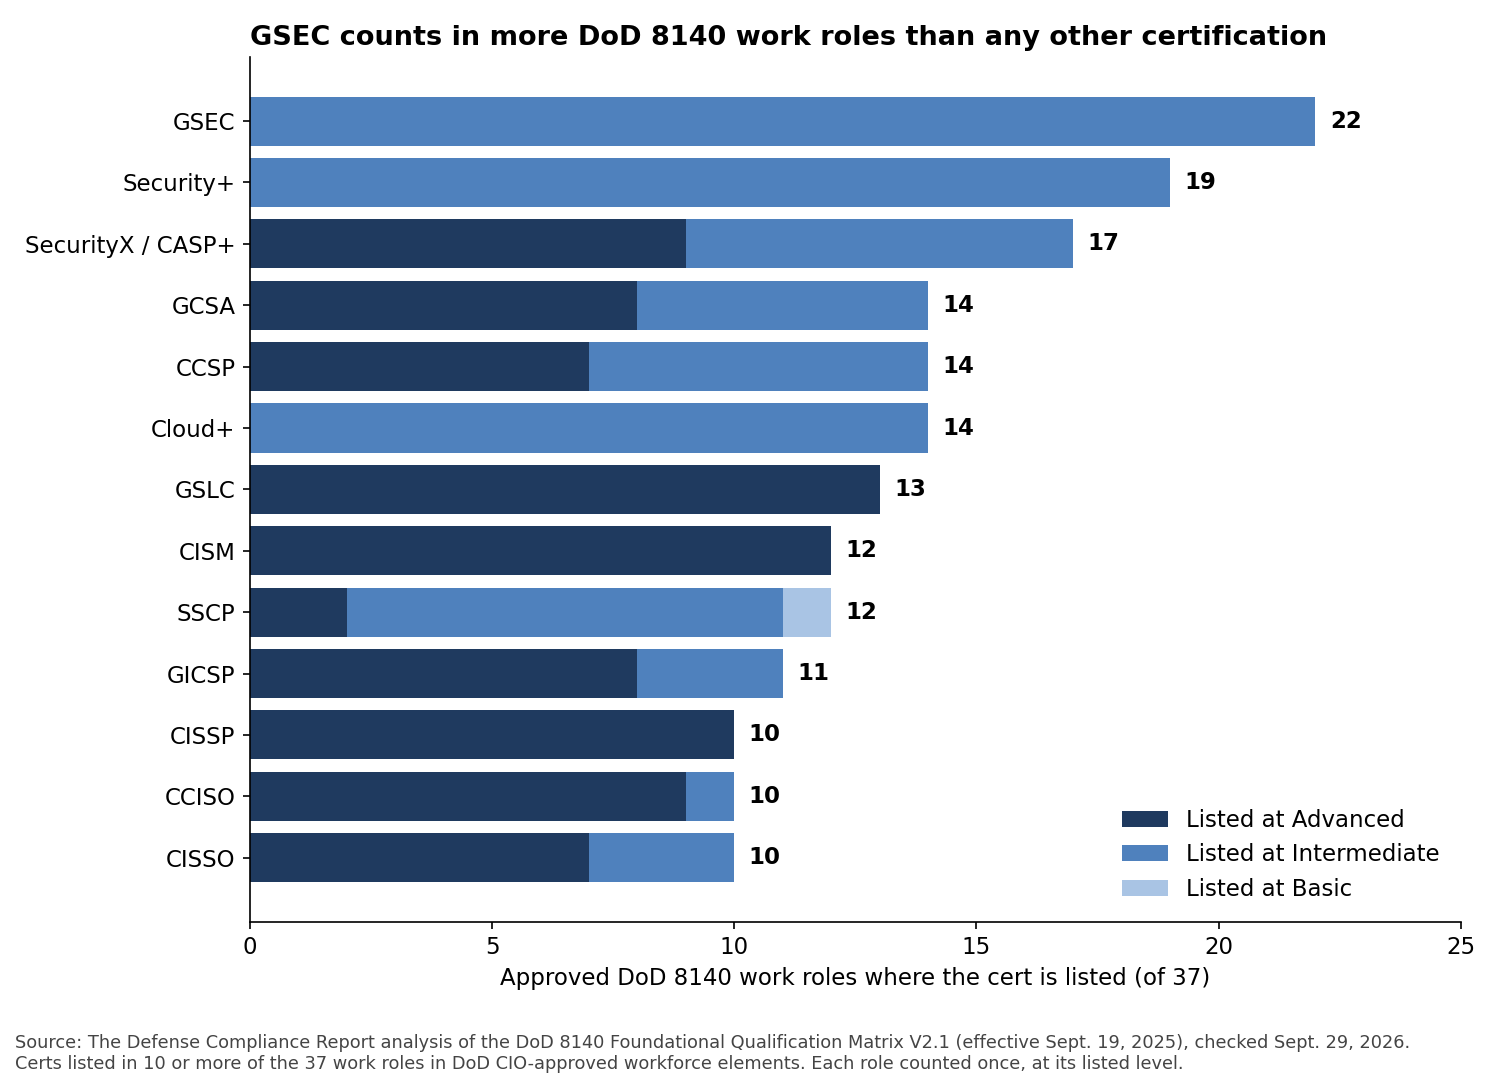
GSEC does. It's listed in 22 of the 37 approved work roles, all at Intermediate. Security+ is next at 19, then SecurityX (formerly CASP+) at 17, which is listed at Advanced in 9 of its roles. For Advanced-level listings, GSLC leads with 13 roles and CISM follows with 12.
GSEC has three more listed roles than Security+ in this V2.1 scope. That is a count of listings, not a claim about more jobs or a better certification.
| Cert | Approved work roles (of 37) | Listed at Advanced | Listed at Intermediate | Listed at Basic |
|---|---|---|---|---|
| GSEC | 22 | 0 | 22 | 0 |
| Security+ | 19 | 0 | 19 | 0 |
| SecurityX / CASP+ | 17 | 9 | 8 | 0 |
| GCSA | 14 | 8 | 6 | 0 |
| CCSP | 14 | 7 | 7 | 0 |
| Cloud+ | 14 | 0 | 14 | 0 |
| GSLC | 13 | 13 | 0 | 0 |
| CISM | 12 | 12 | 0 | 0 |
| SSCP | 12 | 2 | 9 | 1 |
| GICSP | 11 | 8 | 3 | 0 |
| CISSP | 10 | 10 | 0 | 0 |
| CCISO | 10 | 9 | 1 | 0 |
| CISSO | 10 | 7 | 3 | 0 |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository sheet; counts by The Defense Compliance Report, checked Sept. 29, 2026. Each role counted once, at its listed level.
GSEC and Security+ don't cover the same roles, either. They overlap in 15 roles. GSEC reaches 7 roles Security+ doesn't, and Security+ reaches 4 that GSEC doesn't.
| Only GSEC counts (7 roles) | Only Security+ counts (4 roles) |
|---|---|
| 611 Authorizing Official/Designated Representative | 431 Knowledge Manager |
| 631 Information Systems Security Developer | 661 Research & Development Specialist |
| 632 Systems Developer | 751 Cyber Workforce Developer and Manager |
| 651 Enterprise Architect | 752 Cyber Policy and Strategy Planner |
| 652 Security Architect | |
| 711 Cyber Instructional Curriculum Developer | |
| 723 COMSEC Manager |
Source: DoD 8140 Foundational Qualification Matrix V2.1; comparison by The Defense Compliance Report, checked Sept. 29, 2026.
These counts measure how many roles list a cert. They don't measure salary, job openings, or how good a cert is. A narrow cert can be exactly right for your role.
Which vendors have the most certs on the list?
GIAC has 19 of the 56 commercial certifications, about 1 in 3. ISC2 has 9 and CompTIA has 7.
| Vendor | Certs on the V2.1 list |
|---|---|
| GIAC | 19 |
| ISC2 | 9 |
| CompTIA | 7 |
| EC-Council | 6 |
| Cisco | 4 |
| FITSI | 4 |
| CertNexus | 2 |
| ISACA | 2 |
| Mile2 | 2 |
| Rocheston | 1 |
| Total | 56 |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Index sheet; count by The Defense Compliance Report, checked Sept. 29, 2026.
Is Security+ enough for DoD 8140?
For 19 roles, it meets the listed foundational certification option up to Intermediate—not every qualification requirement. Security+ is listed in 19 of the 37 approved work roles, always at Intermediate, so it also covers Basic in those roles. It has no Advanced listing in V2.1.
| Code | Work role | Element | Security+ listed at |
|---|---|---|---|
| 411 | Technical Support Specialist | Cyber IT | Intermediate |
| 421 | Database Administrator | Cyber IT | Intermediate |
| 431 | Knowledge Manager | Cyber IT | Intermediate |
| 441 | Network Operations Specialist | Cyber IT | Intermediate |
| 451 | System Administrator | Cyber IT | Intermediate |
| 511 | Cyber Defense Analyst | Cybersecurity | Intermediate |
| 521 | Cyber Defense Infrastructure Support Specialist | Cybersecurity | Intermediate |
| 531 | Cyber Defense Incident Responder | Cybersecurity | Intermediate |
| 541 | Vulnerability Assessment Analyst | Cybersecurity | Intermediate |
| 612 | Security Control Assessor | Cybersecurity | Intermediate |
| 622 | Secure Software Assessor | Cybersecurity | Intermediate |
| 641 | Systems Requirements Planner | Cyber IT | Intermediate |
| 661 | Research & Development Specialist | Cyber IT | Intermediate |
| 671 | System Testing and Evaluation Specialist | Cyber IT | Intermediate |
| 722 | Information Systems Security Manager | Cybersecurity | Intermediate |
| 751 | Cyber Workforce Developer and Manager | Cyber Enablers | Intermediate |
| 752 | Cyber Policy and Strategy Planner | Cyber Enablers | Intermediate |
| 802 | IT Project Manager | Cyber Enablers | Intermediate |
| 805 | IT Program Auditor | Cyber Enablers | Intermediate |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository sheet; checked Sept. 29, 2026.
Say your position is Cyber Defense Analyst (511) at Advanced. Security+ won't cover it. The Advanced list for 511 is CBROPS, CFR, CySA+, GCFA, GCIA, GICSP.
Which DoD 8140 certifications meet the CMMC assessor requirement for Work Role 612?
17 do. The CMMC rule requires a CMMC Certified Assessor (CCA) to hold at least one qualification at the Intermediate level or higher for Security Control Assessor (612), and V2.1 lists 9 certifications at Intermediate and 8 at Advanced for that role. A Lead CCA needs Advanced, which leaves 8.
The rule is 32 CFR 170.11(b)(6) and (b)(10). It points straight at the DoD 8140 framework, which is why this table matters to anyone chasing a CMMC assessor credential.
| Listed level for Work Role 612 | Certs | Count |
|---|---|---|
| Intermediate | CGRC/CAP, CISSO, Cloud+, FITSP-A, GCSA, GSEC, PenTest+, Security+, SecurityX / CASP+ | 9 |
| Advanced | CCISO, CISA, CISM, CISSP, CISSP-ISSEP, CySA+, GSLC, GSNA | 8 |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository sheet; CCA and Lead CCA levels from 32 CFR 170.11 (eCFR, current to Sept. 25, 2026); checked Sept. 29, 2026.
V2.1 changed this list. It moved CISSO, FITSP-A, and GCSA from Advanced down to Intermediate for 612, and it removed CPTE from 612. So the Advanced list, the one a Lead CCA needs, went from 12 certifications to 8. The CCA list (Intermediate or higher) went from 18 to 17.
A match here covers one gate, not the whole credential. A CCA also needs an active CCP, at least 3 years of cybersecurity experience, at least 1 year of assessment or audit experience, the required training and exam, and a favorable Tier 3 determination (or a DoD-approved equivalent when Tier 3 is not available to that candidate). Tier 3 does not grant a security clearance. Our guide on how to become a CMMC assessor (CCA) walks through the other gates. ISACA's CCA page lists an active CCP, the required CCA course, and an 8140 certification as exam-registration prerequisites; confirm your credential there before you pay.
What certifications does an ISSM need under DoD 8140?
For Information Systems Security Manager (722), V2.1 lists 20 certifications: 1 at Basic, 11 at Intermediate, and 8 at Advanced. Once higher listings roll down, 20 count at Basic, 19 at Intermediate, and 8 at Advanced.
| Listed level for Work Role 722 | Certs | Count |
|---|---|---|
| Basic | CC | 1 |
| Intermediate | CCISO, CCSP, CGRC/CAP, CISSO, Cloud+, GCSA, GMON, GSEC, Security+, SecurityX / CASP+, SSCP | 11 |
| Advanced | CISM, CISSP, CISSP-ISSMP, FITSP-M, GCIA, GCIH, GICSP, GSLC | 8 |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Repository sheet; checked Sept. 29, 2026.
Notice that CISSP and CISM sit in the Advanced row. If your ISSM position is coded Intermediate, Security+ or GSEC also counts.
What happened to the DoD 8570 chart and IAT Level II?
DoD Manual 8140.03 took effect Feb. 15, 2023, and canceled the 8570 manual. Of the 35 certifications on the January 30, 2024 archived 8570 baseline chart, 32 also appear in the V2.1 workbook, some under new names. HCISPP, SCYBER, and CCNA-Security are not.
The big change isn't the cert names. It's the boxes. The 8570 chart sorted people into categories like IAT Level II and IAM Level I. The V2.1 workbook registers 74 work roles and uses Basic, Intermediate, and Advanced levels. That is the register in this release, not a count of every current DCWF role. So "8140 IAT Level II" isn't a real thing. The question is always: which work role code, at which level?
Many charts shared online still show the old IAT and IAM boxes with an 8140 label on top. An IAT or IAM table describes the legacy system; it is not the current work-role matrix.
| Old IAT Level II cert | Still on the 8140 list? | 8140 approved work roles |
|---|---|---|
| CCNA-Security | No | — |
| CySA+ | Yes | 8 |
| GICSP | Yes | 11 |
| GSEC | Yes | 22 |
| Security+ CE | Yes | 19 |
| CND | Yes | 9 |
| SSCP | Yes | 12 |
Source: DoD Approved 8570 Baseline Certifications (archived page); DoD 8140 Matrix V2.1; comparison by The Defense Compliance Report, checked Sept. 29, 2026.
| Cert on the old 8570 chart | 8570 categories | On V2.1? | V2.1 label | V2.1 approved work roles | Note |
|---|---|---|---|---|---|
| A+ CE | IAT I | Yes | A+ | 3 | |
| Network+ CE | IAT I | Yes | Network+ | 5 | |
| SSCP | IAT I, IAT II, CSSP Infrastructure Support | Yes | SSCP | 12 | |
| CND | IAT I, IAT II, IAM I, CSSP Infrastructure Support | Yes | CND | 9 | |
| CCNA-Security | IAT I, IAT II, CSSP Analyst, CSSP Incident Responder | No | — | — | Not on V2.1. Cisco retired it; plain CCNA is on V2.1 for 1 role (441). |
| CySA+ | IAT II, CSSP Analyst, CSSP Infrastructure Support, CSSP Incident Responder, CSSP Auditor | Yes | CySA+ | 8 | |
| GICSP | IAT II, CSSP Analyst, CSSP Infrastructure Support | Yes | GICSP | 11 | |
| GSEC | IAT II | Yes | GSEC | 22 | |
| Security+ CE | IAT II, IAM I | Yes | Security+ | 19 | |
| CASP+ CE | IAT III, IAM II, IASAE I, IASAE II | Yes | SecurityX / CASP+ | 17 | Renamed SecurityX |
| CCNP Security | IAT III | Yes | CCNP Security | 4 | |
| CISA | IAT III, CSSP Auditor | Yes | CISA | 6 | |
| CISSP (or Associate) | IAT III, IAM II, IAM III, IASAE I, IASAE II | Yes | CISSP | 10 | V2.1 lists CISSP; the name comparison does not establish acceptance of Associate status |
| GCED | IAT III | Yes | GCED | 4 | |
| GCIH | IAT III, CSSP Analyst, CSSP Incident Responder | Yes | GCIH | 6 | |
| CCSP | IAT III, IASAE III | Yes | CCSP | 14 | |
| CAP | IAM I, IAM II | Yes | CGRC/CAP | 5 | Renamed CGRC |
| Cloud+ | IAM I, CSSP Analyst, CSSP Infrastructure Support | Yes | Cloud+ | 14 | |
| GSLC | IAM I, IAM II, IAM III | Yes | GSLC | 13 | |
| HCISPP | IAM I, IAM II | No | — | — | Not on V2.1. |
| CISM | IAM II, IAM III, CSSP Manager | Yes | CISM | 12 | |
| CCISO | IAM II, IAM III, CSSP Manager | Yes | CCISO | 10 | |
| CSSLP | IASAE I, IASAE II | Yes | CSSLP | 4 | |
| CISSP-ISSAP | IASAE III | Yes | CISSP-ISSAP | 4 | |
| CISSP-ISSEP | IASAE III | Yes | CISSP-ISSEP | 9 | |
| CEH | CSSP Analyst, CSSP Infrastructure Support, CSSP Incident Responder, CSSP Auditor | Yes | CEH | 7 | |
| CFR | CSSP Analyst, CSSP Infrastructure Support, CSSP Incident Responder, CSSP Auditor | Yes | CFR | 9 | |
| CCNA Cyber Ops | CSSP Analyst, CSSP Incident Responder | Yes | CBROPS | 2 | Renamed CyberOps Associate |
| GCIA | CSSP Analyst | Yes | GCIA | 7 | |
| SCYBER | CSSP Analyst, CSSP Incident Responder | No | — | — | Not on V2.1. |
| PenTest+ | CSSP Analyst, CSSP Incident Responder, CSSP Auditor | Yes | PenTest+ | 9 | |
| CHFI | CSSP Infrastructure Support, CSSP Incident Responder | Yes | CHFI | 3 | |
| GCFA | CSSP Incident Responder | Yes | GCFA | 5 | |
| GSNA | CSSP Auditor | Yes | GSNA | 3 | |
| CISSP-ISSMP | CSSP Manager | Yes | CISSP-ISSMP | 3 |
Source: January 30, 2024 archived DoD chart and V2.1 workbook, checked Sept. 29, 2026. We matched renamed certs to their current labels: CASP+ to SecurityX, CAP to CGRC, and CCNA Cyber Ops to CyberOps Associate.
The two snapshots differ in another way. 24 of V2.1's 56 commercial certifications are absent from the January 30, 2024 archived 8570 chart: CC, CCNA, CCNP Enterprise, CEH(P), CISSO, CPTE, CSC, ECIH, FITSP-A, FITSP-D, FITSP-M, FITSP-O, GCFE, GCLD, GCSA, GCTI, GDSA, GFACT, GISF, GMON, GPEN, GREM, GRID, RCCE Level 1.
That does not make all 24 new to 8140. The archived DoD page says GISF had been on the 8570 approved list and was removed on January 25, 2013. The comparison above tests names in two dated snapshots, not every past approval. Matching a name also does not convert an old category or an Associate status into a current qualification. Archived source.
What changed in DoD 8140 matrix Version 2.1?
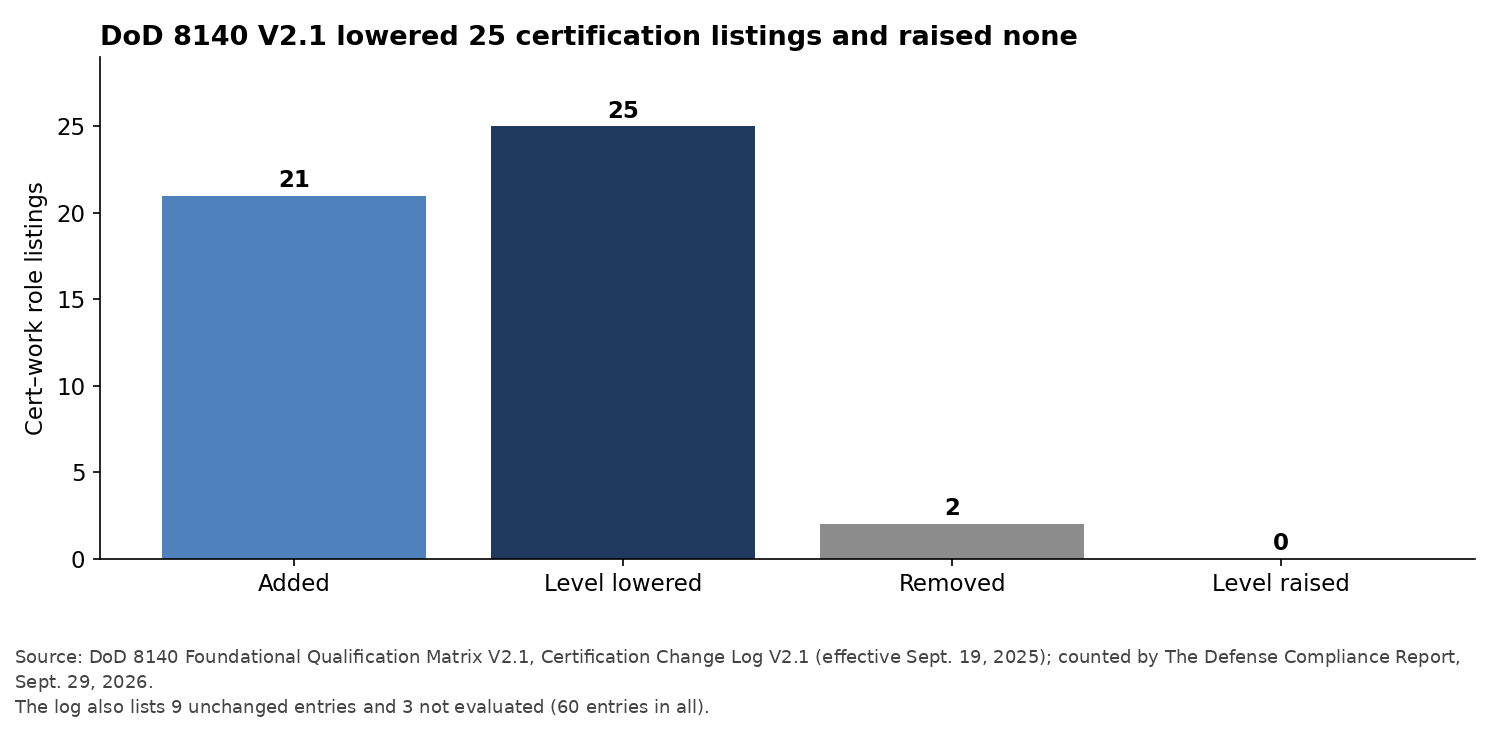
V2.1 took effect Sept. 19, 2025. Its certification change log has 60 entries: 21 listings added, 25 moved to a lower level, 2 removed, 9 unchanged, and 3 not evaluated. No listing moved up.
"Moved to a lower level" means DoD now lists that cert for a lower level in that one role. For example, GCSA for Security Control Assessor (612) went from Advanced to Intermediate. It remains listed for 612 at Intermediate. It no longer appears as a new Advanced option in V2.1; documented qualification under an earlier matrix is a separate question.
The most-added cert was ISC2's Certified in Cybersecurity (CC). It gained Basic listings in 5 roles. The earlier Matrix 2.0 (effective March 25, 2025) changed training content only; DoD said it made no updates to certifications.
This table shows the V2.1 list, not an individual's status. The September 2026 guidance preserves a documented foundational baseline while the member stays in the same role and level and meets annual professional-development requirements. A role or level change, or failure to meet those annual requirements, triggers qualification against the current matrix. Required upskilling still applies.
| Entry type in the V2.1 certification change log | Entries |
|---|---|
| Added | 21 |
| Level lowered | 25 |
| Removed | 2 |
| Level raised | 0 |
| No change | 9 |
| Not evaluated | 3 |
| Total entries | 60 |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Change Log V2.1 sheet; counted by The Defense Compliance Report, checked Sept. 29, 2026.
| Code | Work role | Cert | V2.0 level | V2.1 level | Change |
|---|---|---|---|---|---|
| 212 | Cyber Defense Forensics Analyst | GREM | Not listed | Advanced | Added |
| 212 | Cyber Defense Forensics Analyst | RCCE Level 1 | Not listed | Intermediate | Added |
| 511 | Cyber Defense Analyst | CC | Not listed | Basic | Added |
| 511 | Cyber Defense Analyst | CEH(P) | Not listed | Intermediate | Added |
| 511 | Cyber Defense Analyst | FITSP-O | Advanced | Intermediate | Level lowered |
| 511 | Cyber Defense Analyst | GDSA | Advanced | Intermediate | Level lowered |
| 511 | Cyber Defense Analyst | GFACT | Intermediate | Basic | Level lowered |
| 511 | Cyber Defense Analyst | GISF | Intermediate | Basic | Level lowered |
| 511 | Cyber Defense Analyst | GMON | Not listed | Intermediate | Added |
| 511 | Cyber Defense Analyst | GRID | Not listed | Intermediate | Added |
| 521 | Cyber Defense Infrastructure Support Specialist | CC | Not listed | Basic | Added |
| 521 | Cyber Defense Infrastructure Support Specialist | GCLD | Advanced | Basic | Level lowered |
| 521 | Cyber Defense Infrastructure Support Specialist | GDSA | Advanced | Basic | Level lowered |
| 521 | Cyber Defense Infrastructure Support Specialist | GFACT | Intermediate | Basic | Level lowered |
| 521 | Cyber Defense Infrastructure Support Specialist | GMON | Not listed | Intermediate | Added |
| 521 | Cyber Defense Infrastructure Support Specialist | GRID | Not listed | Intermediate | Added |
| 531 | Cyber Defense Incident Responder | CC | Not listed | Basic | Added |
| 531 | Cyber Defense Incident Responder | CEH(P) | Not listed | Intermediate | Added |
| 531 | Cyber Defense Incident Responder | ECIH | Not listed | Intermediate | Added |
| 531 | Cyber Defense Incident Responder | GDSA | Advanced | Basic | Level lowered |
| 531 | Cyber Defense Incident Responder | GISF | Intermediate | Basic | Level lowered |
| 531 | Cyber Defense Incident Responder | GRID | Not listed | Intermediate | Added |
| 531 | Cyber Defense Incident Responder | RCCE Level 1 | Not listed | Intermediate | Added |
| 541 | Vulnerability Assessment Analyst | CEH(P) | Not listed | Intermediate | Added |
| 541 | Vulnerability Assessment Analyst | CISSO | Advanced | Not listed | Removed |
| 541 | Vulnerability Assessment Analyst | CPTE | Advanced | Intermediate | Level lowered |
| 541 | Vulnerability Assessment Analyst | FITSP-A | Advanced | Intermediate | Level lowered |
| 541 | Vulnerability Assessment Analyst | GCSA | Advanced | Intermediate | Level lowered |
| 541 | Vulnerability Assessment Analyst | RCCE Level 1 | Not listed | Intermediate | Added |
| 612 | Security Control Assessor | CISSO | Advanced | Intermediate | Level lowered |
| 612 | Security Control Assessor | CPTE | Advanced | Not listed | Removed |
| 612 | Security Control Assessor | FITSP-A | Advanced | Intermediate | Level lowered |
| 612 | Security Control Assessor | GCSA | Advanced | Intermediate | Level lowered |
| 622 | Secure Software Assessor | CSC | Advanced | Intermediate | Level lowered |
| 622 | Secure Software Assessor | GCLD | Advanced | Basic | Level lowered |
| 622 | Secure Software Assessor | GCSA | Advanced | Intermediate | Level lowered |
| 631 | Information Systems Security Developer | CC | Not listed | Basic | Added |
| 631 | Information Systems Security Developer | GCSA | Advanced | Intermediate | Level lowered |
| 652 | Security Architect | CCNP Enterprise | Not listed | Advanced | Added |
| 652 | Security Architect | CISSO | Advanced | Intermediate | Level lowered |
| 652 | Security Architect | FITSP-D | Advanced | Intermediate | Level lowered |
| 652 | Security Architect | GCLD | Advanced | Basic | Level lowered |
| 652 | Security Architect | GCSA | Advanced | Intermediate | Level lowered |
| 652 | Security Architect | GMON | Not listed | Intermediate | Added |
| 722 | Information Systems Security Manager | CC | Not listed | Basic | Added |
| 722 | Information Systems Security Manager | CISSO | Advanced | Intermediate | Level lowered |
| 722 | Information Systems Security Manager | GCSA | Advanced | Intermediate | Level lowered |
| 722 | Information Systems Security Manager | GMON | Not listed | Intermediate | Added |
Source: DoD 8140 Foundational Qualification Matrix V2.1, Certification Change Log V2.1 sheet; checked Sept. 29, 2026. The 9 unchanged and 3 not-evaluated entries are in the change-log CSV.
How does DoD 8140 qualification work?
DoD civilians and service members qualify in two steps. First comes one foundational option: a degree, DoD or military training, commercial training, or a certification from the matrix. Then comes resident, on-the-job qualification. Continuous professional development starts in the fiscal year after both are complete: at least 20 hours a year, without excusing any certification body's continuing-education rules. Contractors have the resident-qualification exception below.
Think of foundational qualification as the ticket that gets you into the building. A certification is one way to get that ticket. For civilians and service members, on-the-job sign-off is the badge that lets you work there. They need both steps. All of this comes from DoD Manual 8140.03.
The three levels describe the job, not your rank or grade:
- Basic: You know the basic ideas and can do routine work with frequent, specific guidance.
- Intermediate: You know the basics well, need only occasional high-level guidance, and can handle tricky, non-routine situations.
- Advanced: You understand advanced ideas, need little or no guidance, can guide others, and can handle complex, messy situations.
| Who | Rule | Source |
|---|---|---|
| DoD civilians and service members | Foundational qualification within 9 months. The 2026 guidance starts the period at Letter of Designation issuance; letter issuance is at component discretion. The 2023 manual states assignment as the start. | 2026 guidance, pp. 4–5; manual 4.2.a(2)(a) |
| DoD civilians and service members | Resident qualification within 12 months, with the same 2026 Letter of Designation guidance. Confirm the recorded start with the component. | 2026 guidance, pp. 4–5; manual 4.2.a(2)(b) |
| DoD civilians and service members | The normal waiver limit is 6 months, without back-to-back waivers. The guidance includes exceptions for service-member training availability and combat deployment; an extension requires component approval. | 2026 guidance, Appendix A; manual 4.2.c |
| Contractor staff | Foundational qualification when cyber work starts | Manual 4.2.b; 2026 guidance, p. 4 |
| Cybersecurity workforce element | Original program rollout target for DoD civilians and service members: 2 years from Feb. 15, 2023 (Feb. 15, 2025), subject to applicable waivers and later guidance | Manual 4.3.a(1)(a) |
| Cyber IT, cyber effects, intelligence (cyber), and cyber enabler elements | Original program rollout target for DoD civilians and service members: 3 years (Feb. 15, 2026), subject to applicable waivers and later guidance | Manual 4.3.a(1)(b) |
| Personnel subject to the CPD requirement | At least 20 hours of continuous professional development a year; begins in the fiscal year after foundational and resident qualification. Certification continuing-education rules also remain. | Manual 3.2.b(4) |
Source: DoDM 8140.03, effective Feb. 15, 2023; DoD 8140 Supplemental Guidance V1.1, effective September 1, 2026; checked Sept. 29, 2026.
A few more rules from the manual:
- Experience: Experience can stand in for the foundational step only for federal civilians who were already in covered IT, cybersecurity, or enabler positions when the manual took effect, in the absence of a qualifying degree, training, or certification held by that member, subject to the documented experience-evaluation process. It is not a general substitute for new hires or contractors.
- How a cert gets on the list: A certification needs ISO/IEC 17024 accreditation. It also needs an independent review showing it covers at least 70% of the role's core tasks and knowledge, and a vote by DoD's Cyberspace Workforce Management Board.
- Stricter rules: A DoD component can require more than the baseline. For example, it can require two foundational options instead of one.
Do defense contractors follow DoD 8140 or DoD 8570?
DoD's May 27, 2026 contractor memo directs components to ensure contract support meets the qualifications for its assigned DCWF work roles and to update contracts. Contractor staff must meet foundational qualification when cyber work starts. The old 8570 clause still appears on Acquisition.gov, but that page alone does not describe the full current rule.
Here's what each source says.
- The manual: DoDM 8140.03 applies to "personnel who provide contracted services" (section 1.1.b). It says contractors must be fully qualified (1.2.c) and must meet foundational qualification at the start of cyber work (4.2.b). It tells DoD offices to write its requirements into new contracts and contract changes (2.5.h). It also says contract work should name the DCWF work role and proficiency level (3.1.b(2)). Manual.
- The newer memo: The May 27, 2026 memo says class-deviation text removing the old 8570 references and DFARS 252.239-7001 took effect February 1, 2026. It directs components to ensure the specific work-role qualifications are met and to update contracts. Detailed implementation guidance was still under development when the memo was issued.
- The old clause page: DFARS 252.239-7001 still displays its January 2008 wording and cites 8570. That retained webpage is not evidence that the newer direction does not apply, nor does the memo by itself tell you whether a particular existing contract has been amended.
- The limits: Contractor staff cannot use the manual's federal-civilian experience alternative. Resident qualification applies to contractors only when the component requires it and the contract includes that requirement and how it will be met (4.2.b). Manual.
Read the current performance work statement and any modifications. If it still names 8570 categories like IAT II, the contracting officer can clarify how the newer direction applies to that contract. This is general information, not legal advice.
If you run an IT firm that staffs DoD contracts, our guide to CMMC for IT MSPs covers the company-level rules that sit next to these staffing rules. Subcontractors can check how CMMC flows down to them.
Staff certifications and your company's CMMC status are two separate requirements. If your company also handles controlled unclassified information on DoD contracts, Find My CMMC Path maps your CMMC level and the kind of help to look at first. Do not enter controlled unclassified information or sensitive contract data.
Why does this matter now?
The original rollout targets have passed: Feb. 15, 2025 for cybersecurity roles and Feb. 15, 2026 for the other elements listed in the 2023 manual. Those dates are not a finding that every individual is overdue. The September 2026 guidance addresses individual timelines, waivers, documented baselines, and reporting exemptions for new work roles.
The list also moves. V2.1 lowered 25 listings and removed 2. Four of those changes shrank the Lead CCA list from 12 certs to 8. A chart from even two years ago can steer you wrong, and the old 8570 charts are older still.
How we built this
We started with DoD's V2.1 workbook, linked from the DoD CIO Workforce Innovation Directorate's DoD 8140 Document Library. The library lists a September 30, 2025 upload; the workbook's effective date is September 19, 2025. Each certification record pairs a credential with a work role and a listed level.
- Roles and scope: We matched the 426 records to the workbook's register of 74 work roles. V2.1's published CIO scope covers cybersecurity, cyber IT, and cyber enablers: 37 roles. The other four elements are outside that published scope. Counts use the 384 in-scope records unless they say otherwise; the 42 pending records are retained separately. All 56 commercial labels are in the index, but only 55 appear in the in-scope records. The four DAWIA labels are included in credential-row and level-match totals, not in the commercial-cert count or ranking.
- Counting: We counted each credential once per role, at its listed level. For "credentials that count" at each level, we applied the manual's same-role rule (section 3.2.b(1)(c)5.a). The 36 Basic, 160 Intermediate, and 188 Advanced in-scope records produce 36 × 1 + 160 × 2 + 188 × 3 = 920 matches, including 536 inherited matches. The 111 possible role-level slots are 37 roles × 3 levels. Table 1 ranks only the 56 commercial labels, using shared ranks for ties; the summary CSV uses the same population.
- Checks: We read the official workbook through a document-extraction service, independently keyed its Certification Repository records by role, credential, and level, and compared all 426 keys with our dataset. All matched. We recomputed all 920 level matches and checked the role counts, credential counts, vendor totals, rankings, chart values, and displayed subsets. We did not verify the raw file hash, Reference-sheet cell addresses, or every selectable Matrix Tool view. The files now use verified record locators rather than unverified cell addresses. The official Matrix and Repository SOP says the Matrix controls if it conflicts with the Repository.
- Changes: We classified all 60 entries in the workbook's Certification Change Log V2.1. The 48 changed entries are 21 additions + 25 level changes + 2 removals. The 25 level changes are 16 Advanced-to-Intermediate + 5 Advanced-to-Basic + 4 Intermediate-to-Basic. The log also has 9 unchanged and 3 not-evaluated entries. The earlier 612 totals—12 at Advanced and 18 at Intermediate or higher—are reconstructed from that log, not from a separate full V2.0 workbook comparison. A record absent from the log is labeled "No entry," not assumed unchanged.
- 8570 comparison: We read the January 30, 2024, 01:26:54 archived official page, counted its 35 distinct approved-table labels, and compared names with V2.1. We matched CASP+ to SecurityX / CASP+, CAP to CGRC/CAP, CCNA Cyber Ops to CBROPS, and CE labels to the corresponding V2.1 labels. The archive's Auditor cell says "PenTest"; its provider list identifies PenTest+, so these count as one. The CISSP name match does not establish acceptance of Associate status. There are 32 shared labels, 3 archive-only labels, and 24 V2.1 commercial labels absent from that snapshot. This is not an all-history comparison or a work-role qualification crosswalk.
Every CSV row carries its source, record locator, and check date (Sept. 29, 2026). Source labels are retained for matching. Short names in Table 1 are display labels; the CSV retains the source's certification name. The source spells one label "DAWIA PM Practioner"; the readable name uses "Practitioner." Vendor names are shortened consistently, such as GIAC, ISC2, and CompTIA. Raw source spelling is not proof of a vendor's current marketing name.
What this data does and doesn't show
It shows the certification path only. Degrees, DoD training, and commercial training can also qualify someone, and the Cyber 101 course covers enabler roles.
It doesn't decide whether a person is qualified. That also involves any required resident, on-the-job qualification, stricter component rules, and review of the person's records, including a documented baseline under an older list. Contractor resident requirements have the contract-specific exception explained above.
The 42 pending-validation records are the status of this V2.1 workbook, not a ruling on every other office's current qualifications. They may change. Role counts measure breadth, not salary, job demand, or quality. We use the cert labels DoD uses, so a few names differ from vendor marketing (for example, "SecurityX / CASP+").
How to cite this page
The Defense Compliance Report Editorial Team. "DoD 8140 Certification List and Chart: 56 Certs by Work Role." The Defense Compliance Report. Analysis of DoD 8140 Foundational Qualification Matrix V2.1 (effective Sept. 19, 2025); sources checked Sept. 29, 2026. https://thedefensecompliancereport.com/research/dod-8140-certification-list/
The certification mappings come from the U.S. Department of Defense's public matrix. You're welcome to reuse our counts, tables, charts, and CSV files with credit to The Defense Compliance Report. Keep DoD's attribution and all underlying source terms. Permission covers only DCR's original contribution, not third-party logos, course materials, or other rights we do not own; a link is not required.
Download the data
Six free CSV files, no sign-up. Each row carries its source and check date.
- dod-8140-certification-matrix-v2.1.csv: every cert, work role, and listed level (426 rows)
- dod-8140-level-matches-v2.1.csv: every cert that counts at each level of each approved role, marked "listed" or "counts from a higher level" (920 rows)
- dod-8140-certification-coverage-summary.csv: one row per credential label, including DAWIA, with role counts (60 rows)
- dod-8140-work-roles-cert-options.csv: one row per work role (74 rows)
- dod-8570-to-8140-crosswalk.csv: every cert in the January 30, 2024 archived 8570 chart and its name match in V2.1—not a qualification crosswalk (35 rows)
- dod-8140-v2.0-to-v2.1-changes.csv: DoD's V2.1 change log, classified (60 rows)
DoD 8140 certification FAQ
What certifications are approved under DoD 8140?
The V2.1 workbook (effective Sept. 19, 2025) lists 56 commercial certifications plus 4 DAWIA credential labels. Of the 56 commercial certs, 55 appear in the 37-role published CIO scope; GCTI appears only in pending records. A listed option applies to its assigned role and level, not every role. See Table 1 for the full list.
What are the approved work roles for DoD 8140 certifications?
37 roles sit in the three elements in V2.1's published CIO scope: cybersecurity (13), cyber IT (10), and cyber enablers (14). 34 list at least one certification. Another 37 roles in that workbook register are outside this published scope; that is not a count of all current DCWF roles. Source.
What is DoD 8140?
It's DoD's program for qualifying its cyber workforce by work role, set out in DoD Manual 8140.03, effective Feb. 15, 2023. It replaced the DoD 8570 manual.
Did DoD 8140 replace DoD 8570?
Yes. DoDM 8140.03 took effect Feb. 15, 2023, and canceled DoD 8570.01-M. The May 27, 2026 contractor memo also addresses the move to DCWF qualifications; the still-visible old 8570 clause page is not the whole current rule. Memo.
What is the difference between DoD 8570 and DoD 8140?
8570 sorted people into categories like IAT and IAM with one short cert list. 8140 uses work-role codes and three proficiency levels; the V2.1 workbook registers 74 roles. It provides several foundational paths: degrees, training, certifications, and a limited experience alternative. Resident qualification and at least 20 hours of yearly professional development are separate requirements, with the contractor exception described above. Manual.
What is an 8140 IAT Level II certification?
There isn't one; 8140 has no IAT levels. Of the 7 old IAT Level II certs, 6 are still on the 8140 list for specific work roles. CCNA-Security isn't.
Is there an official full list of all DoD 8140 certifications?
Yes. DoD's V2.1 workbook has a Certification Index with 57 entries: 56 commercial certs and a single DAWIA entry. The Certification Repository pairs the labels with roles and listed levels; pending records are not approval decisions. Table 1 and the CSV files turn that into one sortable list.
Is Security+ enough for DoD 8140?
For 19 of the 37 V2.1 in-scope roles, Security+ meets the listed foundational certification option at Basic or Intermediate. It has no Advanced listing in V2.1. That does not establish full qualification. Mappings; manual.
Does a higher-level certification count for lower levels?
Yes, within the same work role (DoDM 8140.03, section 3.2.b(1)(c)5.a). It never carries over to a different role.
What are the DoD 8140 certification requirements for an ISSM?
For Information Systems Security Manager (722), 20 certifications count at Basic, 19 at Intermediate, and 8 at Advanced. The 8 at Advanced are CISM, CISSP, CISSP-ISSMP, FITSP-M, GCIA, GCIH, GICSP, and GSLC.
Which certifications count for the CMMC CCA's Work Role 612 requirement?
17 certifications count at Intermediate or higher for Security Control Assessor (612), which is the bar 32 CFR 170.11 sets for CCAs. 8 count at Advanced, the bar for Lead CCAs.
How long do I have to get qualified?
DoD civilians and service members have 9 months for foundational qualification and 12 months for resident qualification. The September 2026 guidance uses Letter of Designation issuance as the start and leaves issuance at component discretion; confirm the recorded start with the component. Contractor staff must meet foundational qualification when they start cyber work. Guidance.
Do contractors have to follow DoD 8140?
Yes: the manual requires foundational qualification at the start of cyber work, and the May 27, 2026 memo directs components to ensure specific DCWF work-role qualifications are met and to update contracts. A contract still using 8570 wording needs contract-specific clarification; the old webpage alone is not the current rule. Manual; memo.
Is CEH still approved under DoD 8140?
Yes. CEH is listed in 7 approved work roles, and CEH (Practical) in 3.
Does a change in V2.1 mean I'm no longer qualified?
Not by itself. The September 2026 guidance preserves a documented foundational baseline while the member remains in the same role and level and completes annual professional development. Recoding or missed annual requirements triggers qualification against the current matrix; required upskilling still applies. Guidance, pp. 4–6.
Sources
- DoD CIO Workforce Innovation Directorate, DoD 8140 Document Library: V2.1 workbook listed with upload date September 30, 2025; V2.0 marked archive. Latest listed matrix checked September 29, 2026.
- DoD CIO, DoD 8140 Foundational Qualification Matrix V2.1 workbook, effective September 19, 2025: Certification Repository, Certification Index, Matrix Outline & Notes, Component Change Log V2.1, and Certification Change Log V2.1. Source-extracted records and derived counts checked September 29, 2026. Main CSV · Coverage counts.
- DoD CIO, V2.1 matrix companion document, pp. 1–2: effective date, published workforce-element scope, lower-level rule, and Cyber 101. Full text read September 29, 2026.
- DISA DoD Cyber Exchange, DoD 8140 Qualification Matrices. V2.1 notice checked September 29, 2026; current files linked in source 1.
- DoD, DoD Manual 8140.03, Cyberspace Workforce Qualification and Management Program, effective February 15, 2023. Sections 3.2, 3.3, 4.2, and 4.3 support the qualification rules. Full text read September 29, 2026.
- DoD Manual 8140.03, section 4.3, p. 21: original two- and three-year program rollout targets. The derived calendar dates are February 15, 2025 and February 15, 2026. Read September 29, 2026; later guidance is source 12.
- DoD CIO, DoD 8140 Matrix 2.0 Change Management Bulletin, effective March 25, 2025: no education or personnel-certification updates in V2.0. Read September 29, 2026. The V2.1 workbook labels its previous release March 26, 2025; that is a different date label from the bulletin's effective date.
- 32 CFR 170.11, CMMC Certified Assessor, especially (b)(3), (b)(4), (b)(6), and (b)(10). The retrieved eCFR displayed current through September 25, 2026. Full section read September 29, 2026.
- DFARS 252.239-7001, Information Assurance Contractor Training and Certification (January 2008). Retained clause-page wording checked September 29, 2026; it must be read alongside the newer direction in source 13.
- Contractor requirements in DoDM 8140.03, section 4.2.b: foundational requirements at commencement; resident qualification only when required by the component and included in the contract. Read September 29, 2026. Source 13 addresses implementation updates.
- DoD Cyber Exchange, DoD Approved 8570 Baseline Certifications, exact January 30, 2024 archive. Full approved-certification tables, provider list, and GISF/GSE January 25, 2013 removal note read September 29, 2026. Snapshot name comparison CSV.
- DoD 8140, Supplemental Guidance for Cyber Workforce Management V1.1, effective September 1, 2026, pp. 3–8 and Appendix A. Letter of Designation timing, continued baselines, recoding, upskilling, new-role reporting exemptions, and waiver exceptions. Full text read September 29, 2026.
- Chief Information Officer, Implementation of Cyberspace Workforce Policy Requirements for Contractors, May 27, 2026. The memo identifies February 1, 2026 as the effective date of the class-deviation text and directs DCWF qualification and contract updates. Full text read September 29, 2026.
- ISACA, CCA certification: exam-registration prerequisites and certification requirements. Read September 29, 2026. The role/level requirement is also set in source 8.
- DoD CIO, Matrix and Repository SOP, Version 1.1, issued April 19, 2024, p. 8: Matrix takes precedence over Repository discrepancies. Read September 29, 2026.
The Defense Compliance Report is an independent trade publication covering CMMC and Defense Industrial Base compliance.